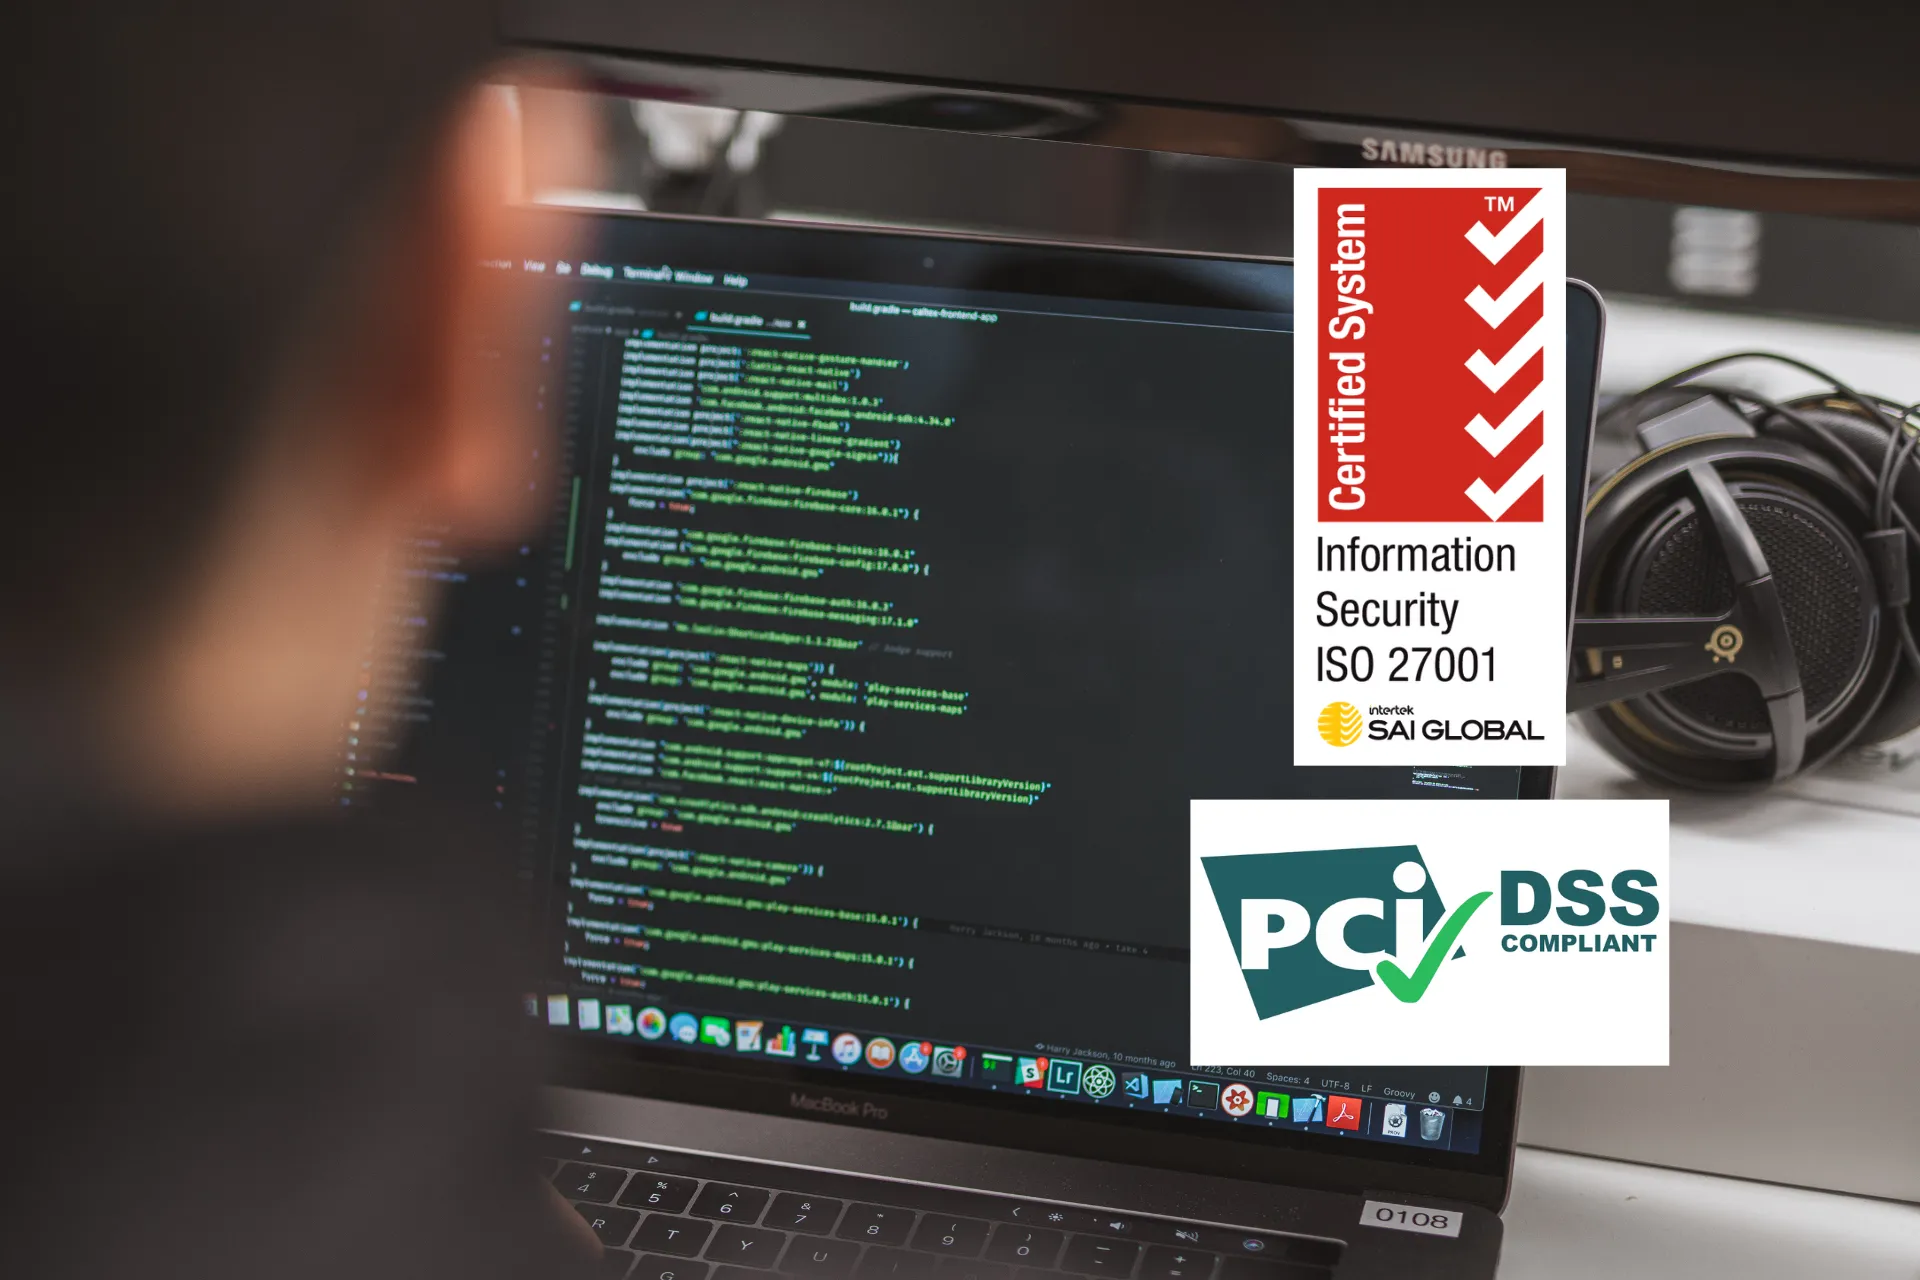




RUSH is certified to ISO/IEC 27001:2022 across the whole business. Our secure development service also holds a PCI DSS v4.0.1 service provider attestation. As far as we are aware, we're the first software development house in Australia and New Zealand to have its development process independently assessed against PCI DSS as a service provider.
"In an era where digital trust is paramount, holding these certifications demonstrates our unwavering commitment to protecting our clients' data. It reflects our values of creating sustainable solutions and maintaining transparent communication with our partners. As we continue to design and build technology that better serves humankind, robust information security practices are fundamental to everything we do." - Danu Abeysuriya, CEO of RUSH.
What each standard covers
ISO 27001 is about how a whole organisation manages information security, from spotting risks to deciding what to do about them and continually improving. Ours covers development, design, support, consulting and strategy. Certification is carried out by independent certification bodies, which in our case is Telarc. We were certified in October 2024, have been audited by Telarc every year since, and are certified until October 2027.
PCI DSS is far more prescriptive. Every requirement is exact, and "mostly" doesn't count. Our assessment was a full Report on Compliance completed by Confide, an independent Qualified Security Assessor, and we were rated compliant with no requirements found not in place. It covers our secure development service, which is how we build bespoke software for clients who need it to meet PCI DSS. That includes how our development workstations are built and managed, our office network controls, logging, protection against malware and phishing, and our code repositories and development process up to the point a client approves a release. Any client can use the service. Releasing to production and running the payment environment stay with the client.
ISO gives clients independent assurance across everything we do. PCI is the extra, independently tested assurance for clients who handle payments.
What it doesn't mean
Our attestation covers how we build. It doesn't mean the system we build for you is PCI compliant the day we hand it over. There's no rubber stamp. Your system still needs its own assessment, but because the process behind it has already been independently tested, a big chunk of that work is done before your assessor arrives.
Our attestation covers how we build, not production. Where we run production environments for clients, those are assessed as part of the client’s own PCI scope.
Built on years of client work
We'd been building and supporting PCI-compliant systems for clients for years before we went for ISO 27001. ISO gave that practice structure across the whole business, and by the time we did our own PCI assessment in 2025, it made evidencing it a whole lot easier. Today it all runs as one system, with the same risk register, policies and audit cycle covering both standards.
"At RUSH, we're united by our love of technology and its potential for making lives better. This certification is a natural extension of that mission. Our clients trust us to create digital products that provide frictionless, inclusive experiences. We're ensuring that security and privacy are seamlessly integrated into every solution we deliver." - Terry Williams-Willcock, CCO
How it works day to day
Every change we make is written to secure coding standards, scanned automatically, peer reviewed, and released only when the client approves it. Aikido covers our code, open-source dependencies, pipelines and cloud configuration, along with static and dynamic application testing. Wiz secures the production cloud environments we run. Live card data stays in our clients' environments, and our own development environment takes a zero-trust approach.
What it means to partner with us
Looking for a partner: your security and procurement teams can start with our ISO certificate, PCI attestation and responsibility matrix, instead of sending hundreds of questions and waiting for answers. If you handle payments, you can rely on our attestation rather than bringing us into your own PCI scope or assessing our development process yourself.
For our partners: nothing changes in how we work with you, because this is how we've been building all along. What's new is the independent evidence behind it, which makes your own vendor reviews and PCI assessments simpler. Ask your RUSH contact for the latest certificate, attestation and responsibility matrix.
Building something that handles payments? Talk to our security team about what you're building.